🚀 Automated CDK Deployment Pipeline
↩️ Back to AWS Cloud Engineering
Overview
A CI/CD pipeline that automates deployment of the AWS Secure Serverless Notes API using GitHub Actions and the AWS CDK. Every change triggers an automated pipeline that installs dependencies, runs unit tests, validates the infrastructure template, and deploys to AWS — authenticating with short-lived federated credentials instead of static access keys.
| Area | Summary |
|---|---|
| Problem | Manual infrastructure deployments are inconsistent, undocumented, and typically rely on long-lived AWS credentials stored on a developer machine. |
| Action | Built a GitHub Actions pipeline that tests, validates, and deploys the CDK stack automatically, authenticating to AWS via a federated OIDC identity instead of stored access keys. |
| Tools / Evidence | GitHub Actions, AWS CDK, IAM OIDC identity provider, CloudFormation, pytest, pipeline run logs, AWS Console deployment confirmation. |
| Control Value | Removes long-lived credentials from the deployment process, blocks deployment on failing tests, restricts deployment trust to a specific repository and branch, and produces an auditable deployment history. |
| Public-Safe Evidence | Pipeline run and console screenshots, with account identifiers removed. |
Pipeline Stages
- Checkout & environment setup — clones the repository, installs Python 3.12
- Dependency installation — installs CDK and test dependencies
- AWS authentication — assumes an IAM role via OpenID Connect (OIDC); no stored credentials
- Unit tests — runs
pytestagainst the stack definition; failing tests block deployment - CDK synth — compiles and validates the CloudFormation template before touching live infrastructure
- CDK deploy — deploys the validated stack to AWS
Key Engineering Decisions
OIDC over static access keys. The pipeline authenticates via an IAM identity provider trusting token.actions.githubusercontent.com, exchanging a short-lived GitHub token for temporary AWS credentials at runtime — eliminating the risk of a leaked or stale access key.
Trust policy scoped to a specific repository and branch. The IAM role’s trust relationship only accepts requests from this exact repository on main, so a fork or unrelated branch cannot assume the role even with the role ARN.
Test-before-deploy gating. Unit tests run before cdk synth/cdk deploy, catching a broken stack definition before any AWS API calls are made.
Path-filtered triggers. The workflow only runs on changes within the Notes API project folder, so unrelated commits elsewhere in the portfolio don’t trigger unnecessary AWS deployments.
Lab Evidence
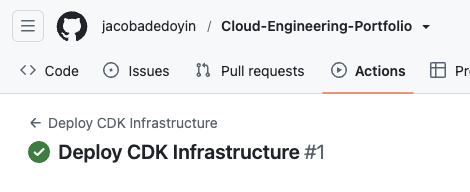
GitHub Actions confirming the pipeline completed successfully
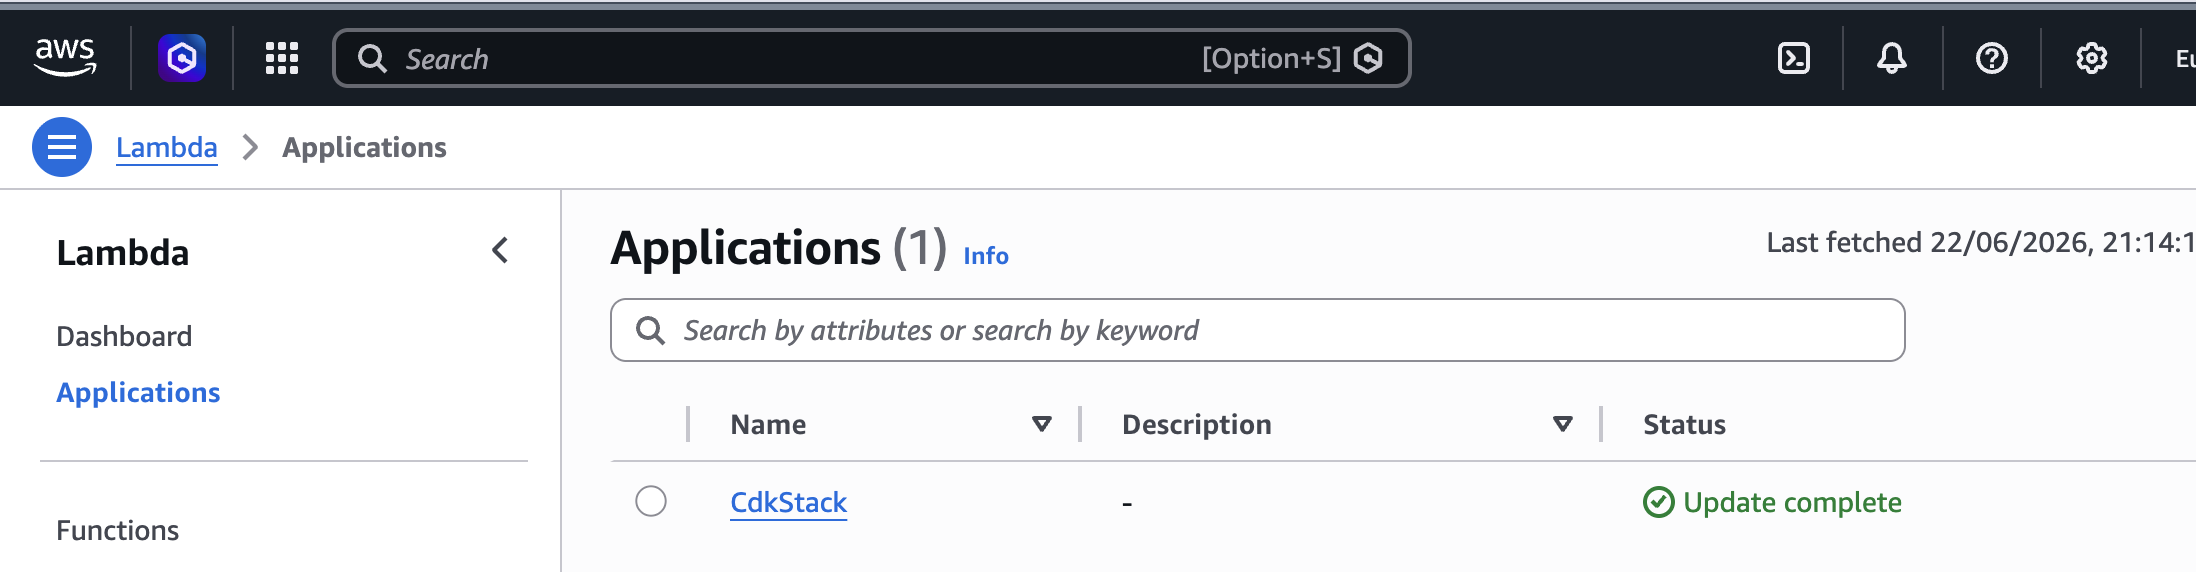
AWS Console showing the CloudFormation stack reached "Update complete"
Skills Demonstrated
AWS CDK GitHub Actions OIDC IAM CloudFormation CI/CD Infrastructure as Code
🔒 All evidence is public-safe, sanitised, and lab-based. No account IDs, secrets, or production data are included.