🔐 MFA Application Deployment and Operations
↩️ Back to Identity & Access Governance Index
📁 Back to Projects Index
Overview
This project demonstrates practical IAM delivery for MFA rollout, secure application access, authentication transition support, and post-deployment operations across Qlik and Tableau data platforms.
The work focused on helping users move through authentication changes safely, reducing access disruption, supporting issue triage, producing user guidance, and improving repeatable support processes after deployment.
Delivery Evidence
| Area | Summary |
|---|---|
| Problem | Users needed secure and reliable access to Qlik and Tableau while MFA and authentication controls were strengthened. |
| Action | Supported MFA rollout activity, user readiness, access issue triage, documentation, stakeholder communication, and post-deployment improvement. |
| Tools / Evidence | MFA, OIDC-based authentication, Qlik, Tableau, IAM support processes, SOPs, FAQs, quick guides, and access support workflows. |
| Control Value | Strengthened authentication, improved secure application access, reduced rollout disruption, and supported repeatable access operations. |
| Public-Safe Evidence | Role summary, skills diagram, project scope, support activities, and documentation examples with sensitive user and platform details removed. |
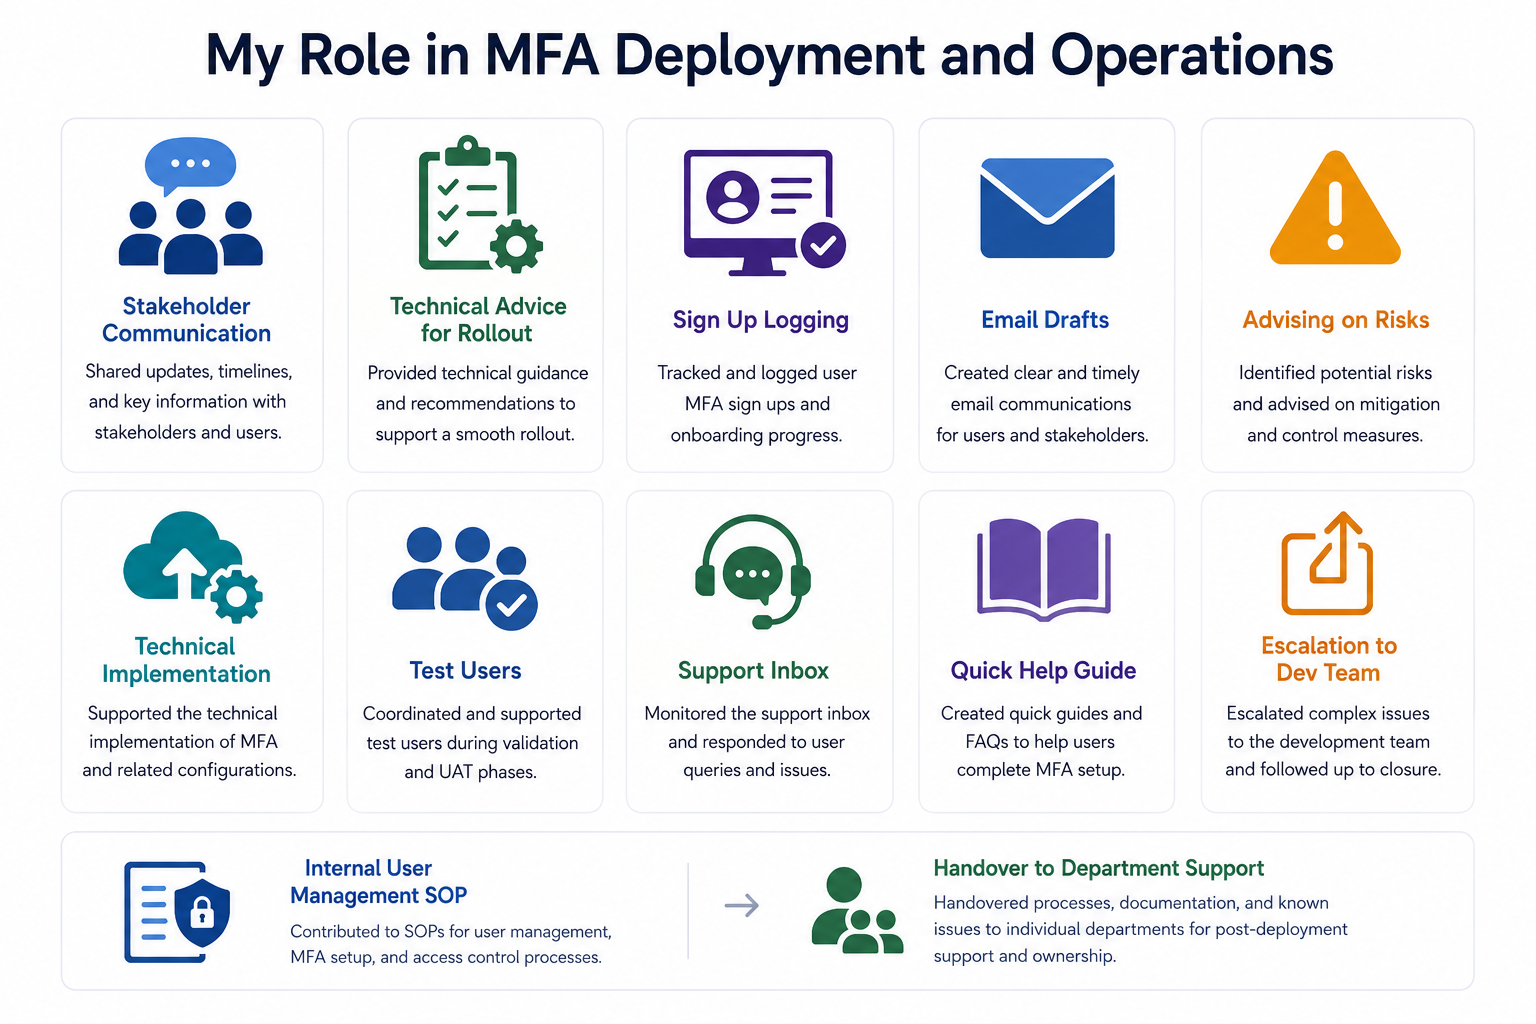
Role Summary
Project Scope
| Area | Evidence of Experience |
|---|---|
| MFA Rollout Support | Helped users prepare for MFA adoption and secure sign-in changes. |
| Application Access | Supported secure access to Qlik and Tableau data platforms. |
| OIDC Transition | Assisted with authentication transition and user readiness activity. |
| Access Issue Triage | Investigated setup, login, and access problems before escalation. |
| Stakeholder Support | Supported communications, guidance, and user-facing rollout activity. |
| Documentation | Contributed to SOPs, FAQs, quick guides, and support handover material. |
| Post-Go-Live Improvement | Identified recurring issues and improvement opportunities after deployment. |
Skills Demonstrated
| Skill Area | Evidence Demonstrated |
|---|---|
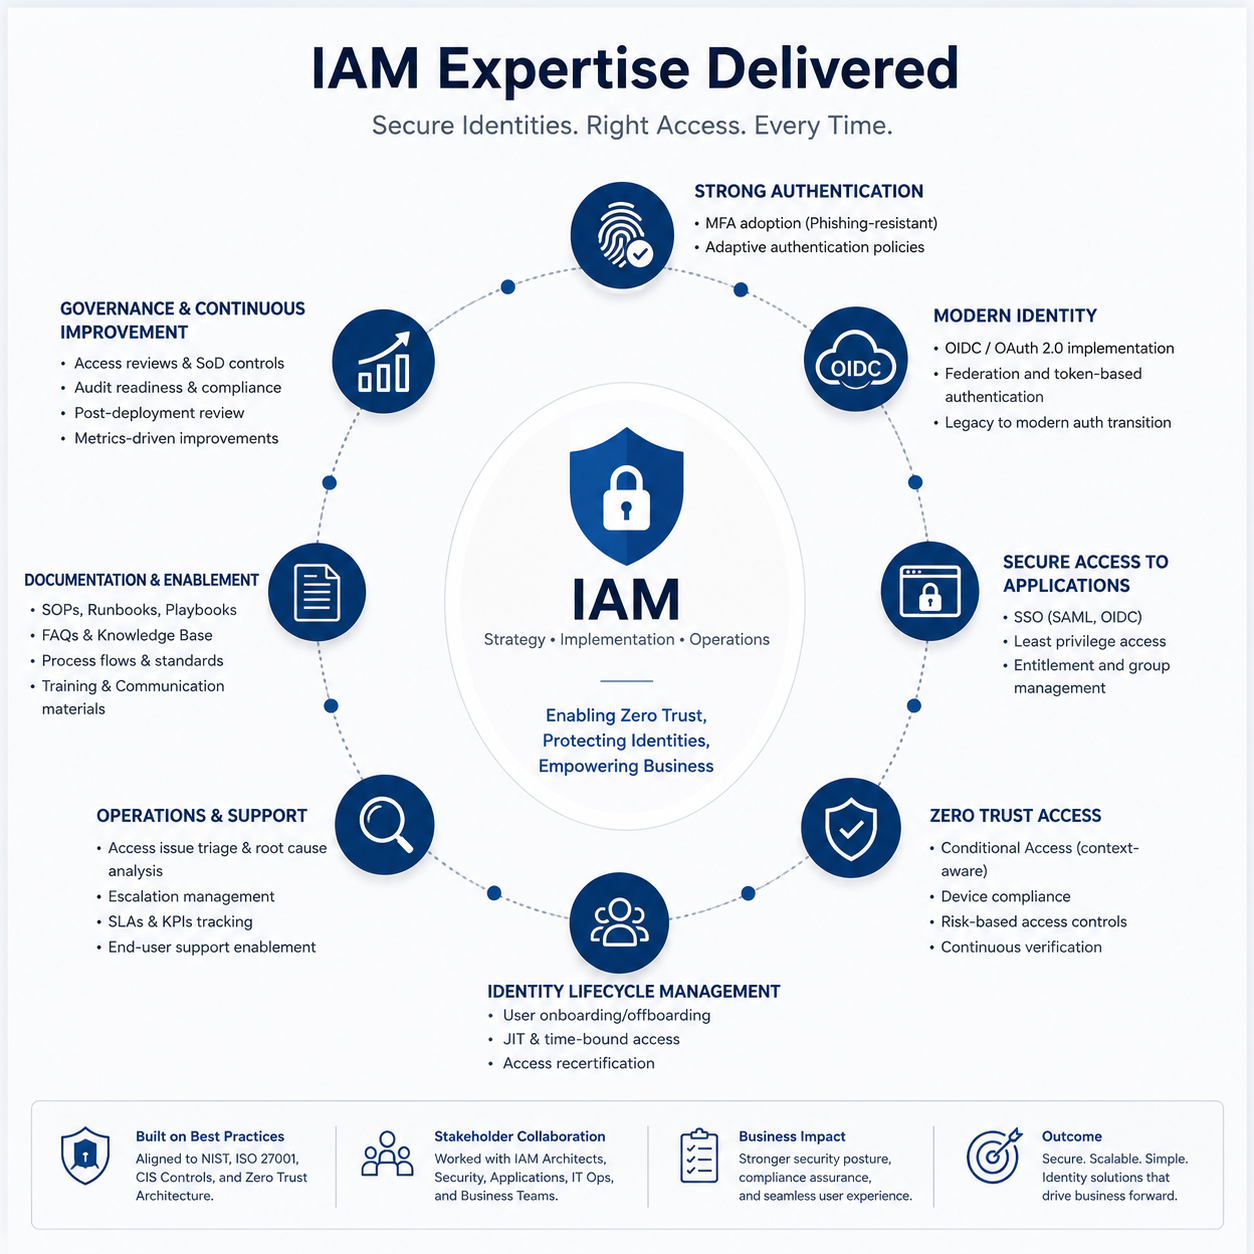
| MFA Deployment Support | Supported users through MFA adoption, secure sign-in changes, and authentication readiness. |
| Application Access Operations | Helped maintain reliable access to Qlik and Tableau while stronger authentication controls were introduced. |
| Authentication Transition Awareness | Worked around OIDC-based authentication changes and supported users during transition activity. |
| Access Issue Triage | Investigated enrolment, login, setup, and access issues before escalation. |
| Stakeholder Communication | Supported clear user-facing communication during rollout and post-deployment activity. |
| Operational Documentation | Contributed to SOPs, FAQs, quick guides, support notes, and handover material. |
| Post-Deployment Improvement | Identified recurring support issues and improvement opportunities after go-live. |
| Public-Safe Evidence Handling | Presented IAM delivery evidence without exposing user, platform, or internal authentication details. |
IAM Skills Demonstrated
Professional Relevance
This project is relevant to IAM Engineer, Application Support, Cloud Security, Security Operations, and data platform access governance roles.
It demonstrates practical ability to support secure application access where authentication changes must be:
- communicated clearly
- adopted by users
- supported during rollout
- triaged when issues occur
- documented for repeatable operations
- improved after deployment
Public-Safe Note
This project uses public-safe and sanitised evidence only. It does not include real user names, internal application URLs, authentication records, screenshots, support tickets, approval records, tenant details, or confidential platform information.