📁 Secure File Transfer Platform Operations
↩️ Back to Identity & Access Governance
📁 Back to Projects Index
Overview
This project demonstrates operational ownership of a secure file transfer platform used to control the movement of sensitive business files.
The work focused on secure platform administration, access control, folder permissions, migration support, joiner/mover/leaver activity, stakeholder guidance, and repeatable operational processes.
Delivery Evidence
| Area | Summary |
|---|---|
| Problem | Sensitive business files needed to be transferred through a controlled platform with appropriate access, permissions, traceability, and operational oversight. |
| Action | Supported secure platform administration, access changes, folder permissions, migration activity, JML processes, stakeholder guidance, and repeatable operational documentation. |
| Tools / Evidence | MOVEit Secure Transfer, access request workflows, permission matrices, migration checklists, IAM processes, and operational support documentation. |
| Control Value | Improved access oversight, supported least privilege, reduced stale access risk, strengthened secure file movement, and improved audit traceability. |
| Public-Safe Evidence | Operations overview, IAM skills diagram, access workflow, request template, migration checklist, and permission matrix template with sensitive platform details removed. |
Operations Overview
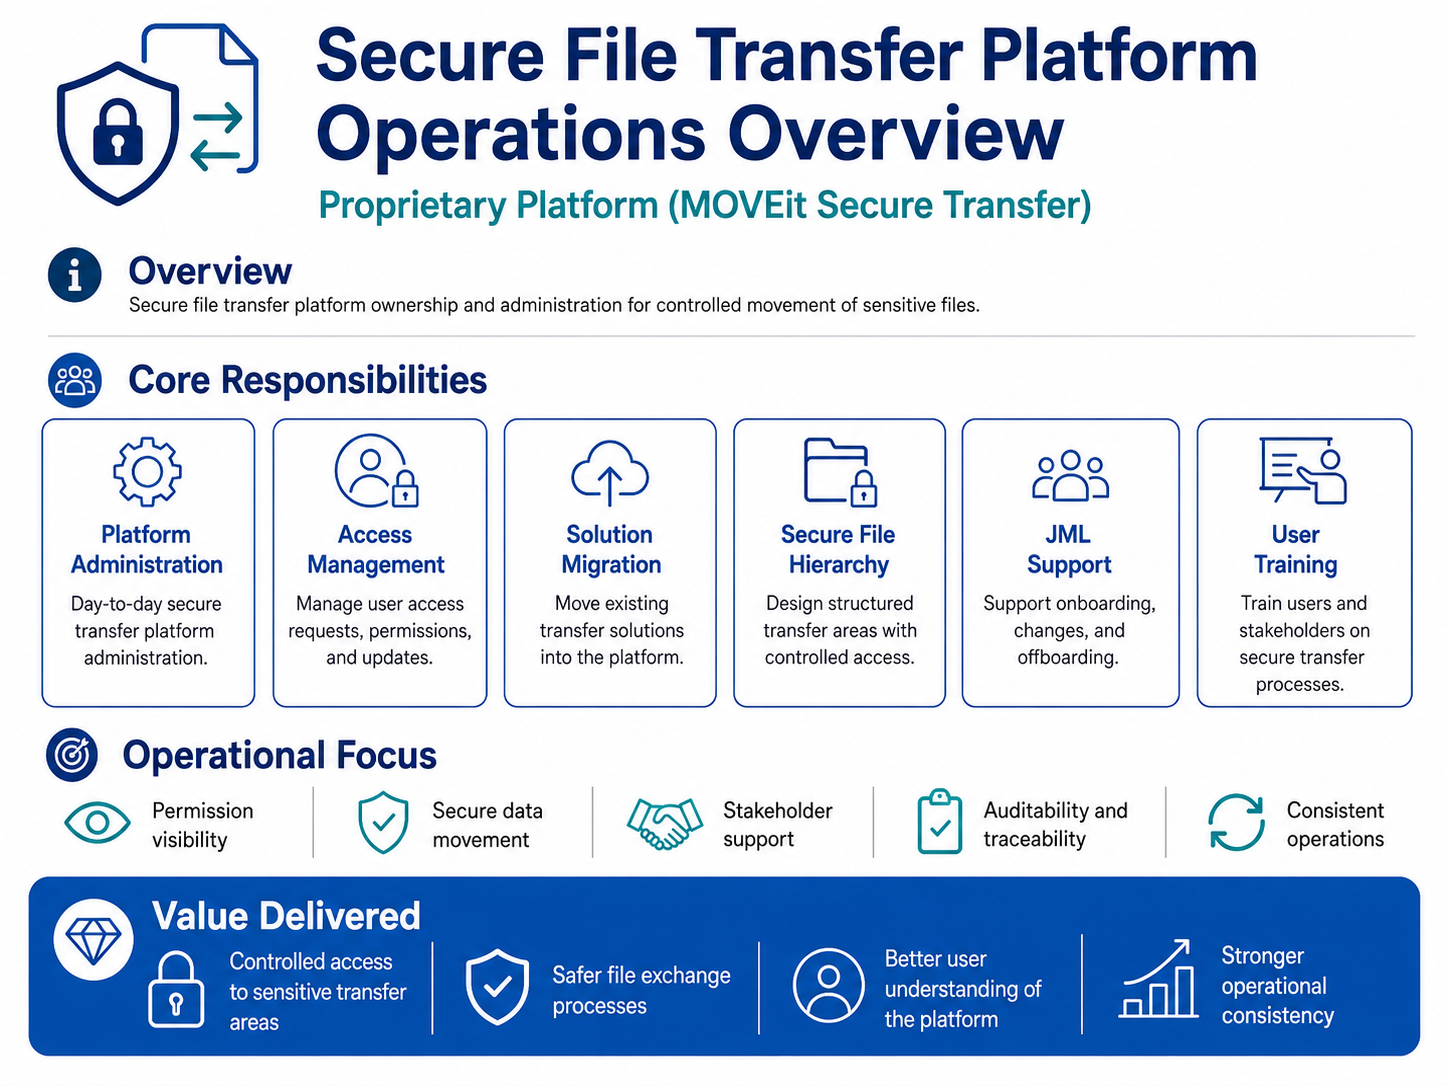
Platform
| Platform | Purpose |
|---|---|
| MOVEit Secure Transfer | Secure file transfer platform used to manage controlled file movement, user access, folder permissions, and operational support activity. |
Skills Demonstrated
| Skill Area | Evidence Demonstrated |
|---|---|
| Secure File Transfer Administration | Supported controlled file movement through a managed secure transfer platform. |
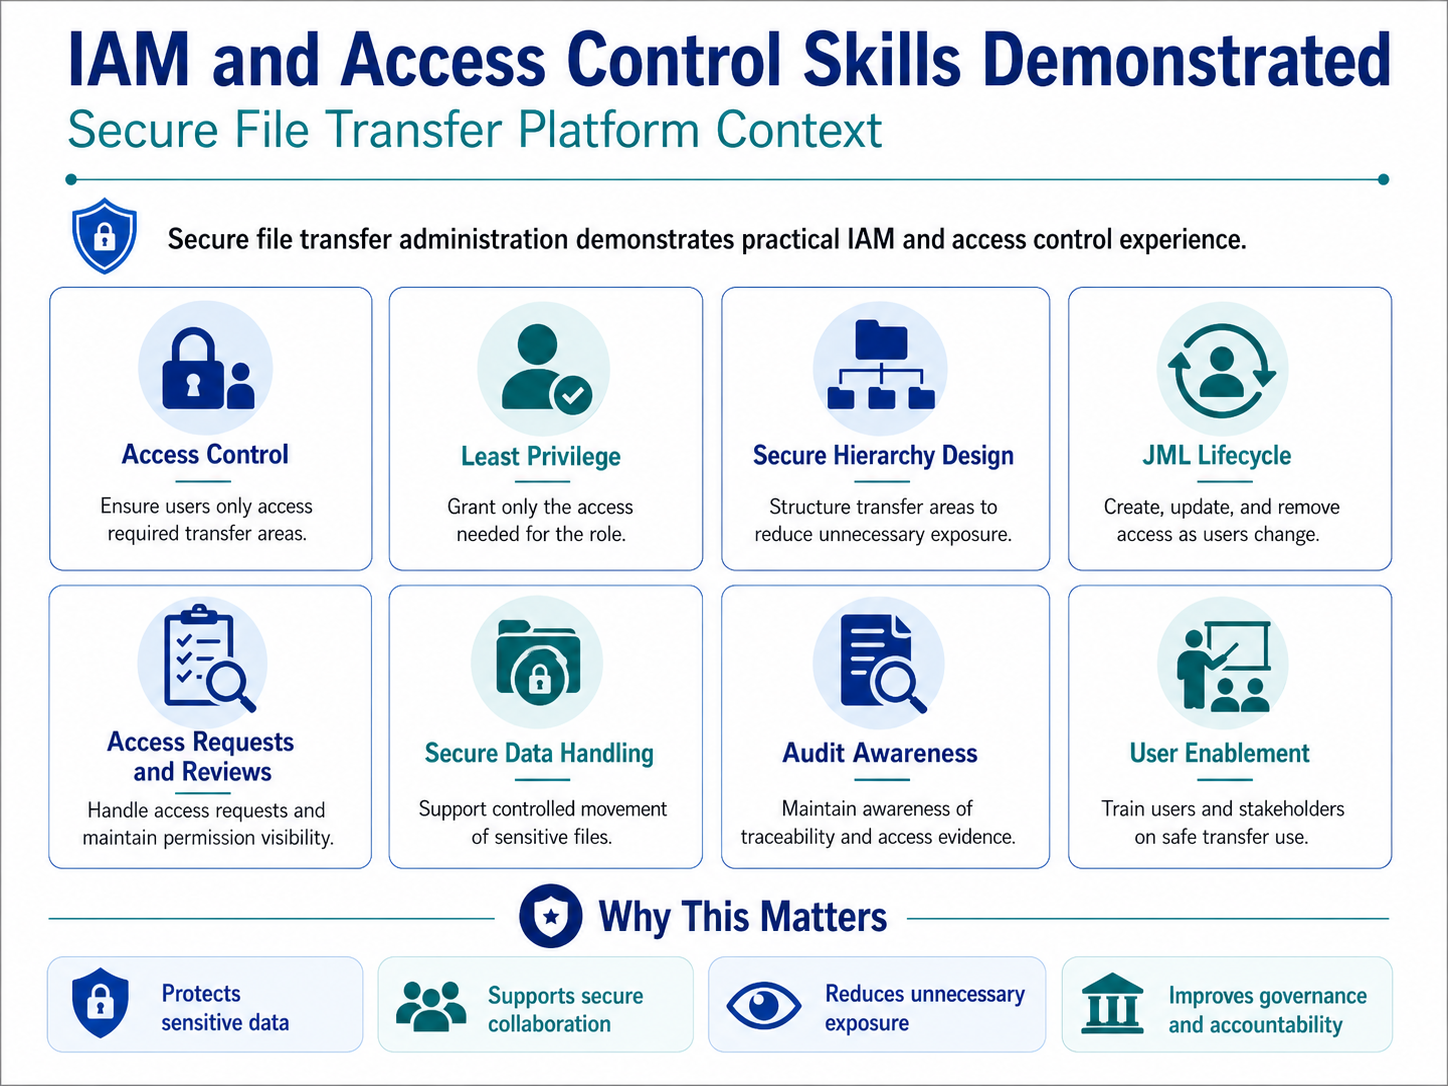
| IAM Operational Support | Managed access-related activity through request handling, user support, and operational controls. |
| Least Privilege Access Control | Supported access decisions based on business need, permission scope, and controlled access principles. |
| Folder-Level Permission Management | Worked with folder access, permission boundaries, and access visibility across platform areas. |
| Joiner, Mover and Leaver Controls | Supported access changes linked to onboarding, role movement, and leaver activity. |
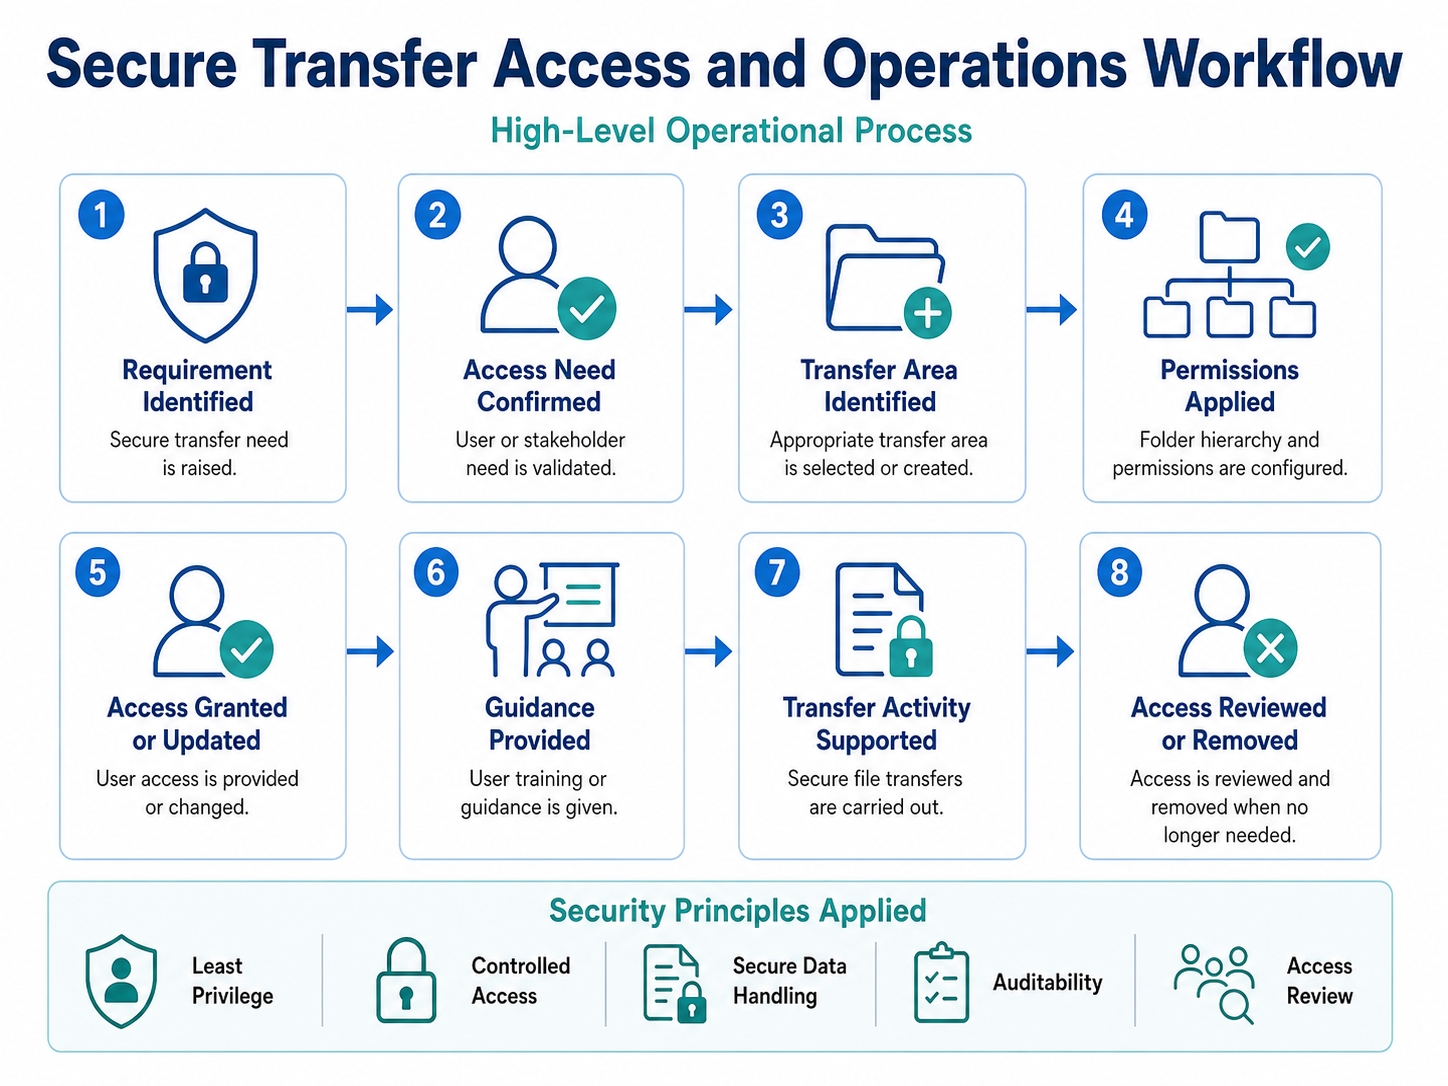
| Access Request Handling | Used structured request processes to support traceable and repeatable access changes. |
| Permission Matrix Design | Produced permission matrix evidence to show how access could be reviewed and controlled. |
| Secure Data Movement Awareness | Demonstrated awareness of confidentiality, traceability, and controlled transfer requirements. |
| Audit and Traceability Awareness | Supported evidence capture and documentation for access, transfer, and operational review. |
| Stakeholder Support | Provided guidance to users, service owners, and stakeholders involved in secure transfer operations. |
| Operational Documentation | Created or maintained public-safe support material, templates, checklists, and process documentation. |
IAM and Security Skills
Operations Workflow
Evidence Pack
| Evidence | Location |
|---|---|
| Operations Overview | secure-file-transfer-operations-overview.png |
| IAM and Access Control Skills | secure-transfer-iam-access-control-skills.png |
| Access Operations Workflow | secure-transfer-access-operations-workflow.png |
| Access Request Template | secure-transfer-access-request-template.md |
| Migration Checklist | secure-transfer-migration-checklist.md |
| Permission Matrix Template | secure-transfer-permission-matrix-template.md |



Professional Relevance
This project is relevant to IAM Engineer, Application Support, Security Operations, Cloud Security, and enterprise platform governance roles.
It demonstrates practical ability to support secure business platforms where file movement must be:
- controlled
- permissioned
- traceable
- documented
- reviewed
- aligned to least privilege
- supported through repeatable operational processes
Public-Safe Note
This project uses recreated and sanitised evidence only. It does not include real platform screenshots, folder paths, file names, user records, transfer logs, IP addresses, internal URLs, credentials, or confidential operational details.